Vietnam ICT Import Rules 2026: New Risk-Based Quality Management Framework
Vietnam’s New Risk-Based Management Framework for Imported ICT Goods from July 2026 1. Introduction: the context of the transformation Prior to 2026, the state management system for the quality of imported information technology and telecommunications goods will operate on a pre-inspection model based on the 2007 Law on Product and Goods Quality. All products capable […]
TCBC April 2026: Regulatory Trends, Emerging Technologies, and the Future of Wireless Compliance
The Wireless Industry Enters a New Compliance Era The TCBC April 2026 workshop brought together regulators, certification bodies, laboratories, and industry participants to discuss ongoing developments in wireless regulation, conformity assessment, cybersecurity, and emerging technologies. While TCBC itself does not create or immediately implement regulations, the workshop provided insight into the direction regulators are considering […]
Moving from Compliance Guesswork to Strategic Classification
In the complex and ever-evolving world of global trade and product compliance, manufacturers frequently grapple with a significant concern: the fear of “missing” a required certification, especially after making seemingly minor design modifications, such as the removal of a specific feature like a wireless radio. This apprehension stems from a common misconception that regulatory compliance […]
Key Updates from TCBC Workshop 2025
Workshop Summary Agenda The TCBC Council Workshop 2025 provides essential updates from North American and international regulators, along with insights into new methods and equipment that help meet industry standards. Cybersecurity remains a central focus, with panel discussions covering product development, manufacturing, testing, and perspectives from Telecommunication Certification Bodies (TCBs). RF Exposure and SAR Simulations […]
Greece CRA risk-based approach: REDCA 50th Meeting News
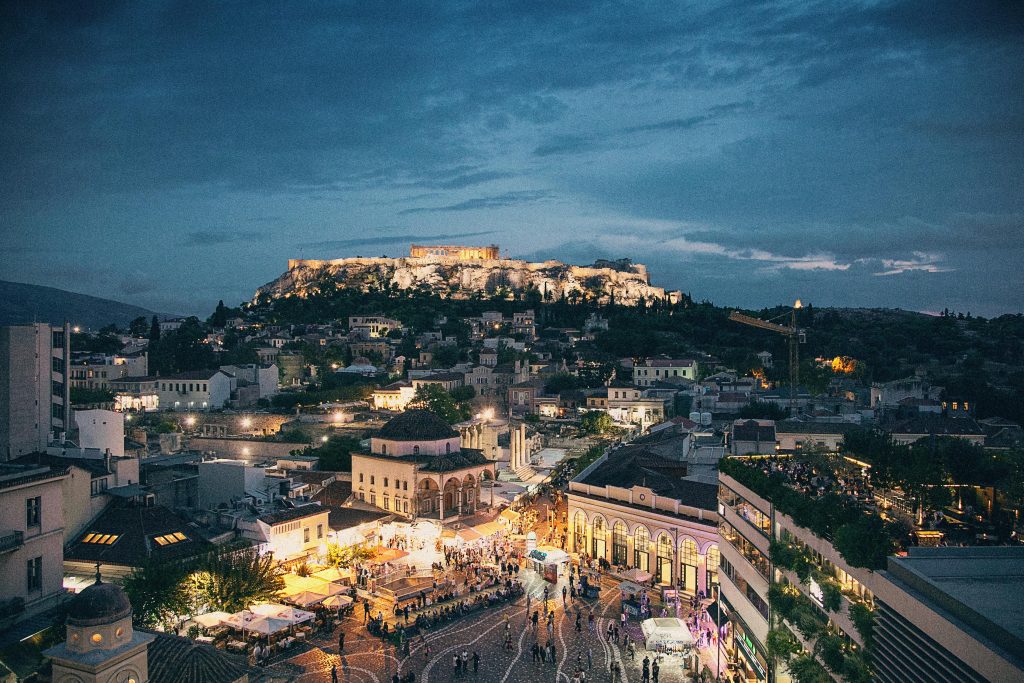
CRA Developments and Regulatory Complexity Discussed in Athens In Greece, the REDCA 50th meeting held in Athens on November 5th and 6th, 2025, highlighted critical updates on the European Union’s Cybersecurity Resilience Act (CRA) and changes in the regulatory environment for radio equipment. This summary outlines the comprehensive details shared during the sessions, focusing particularly […]
GSR 2025 Recommendations from Saudi Arabia
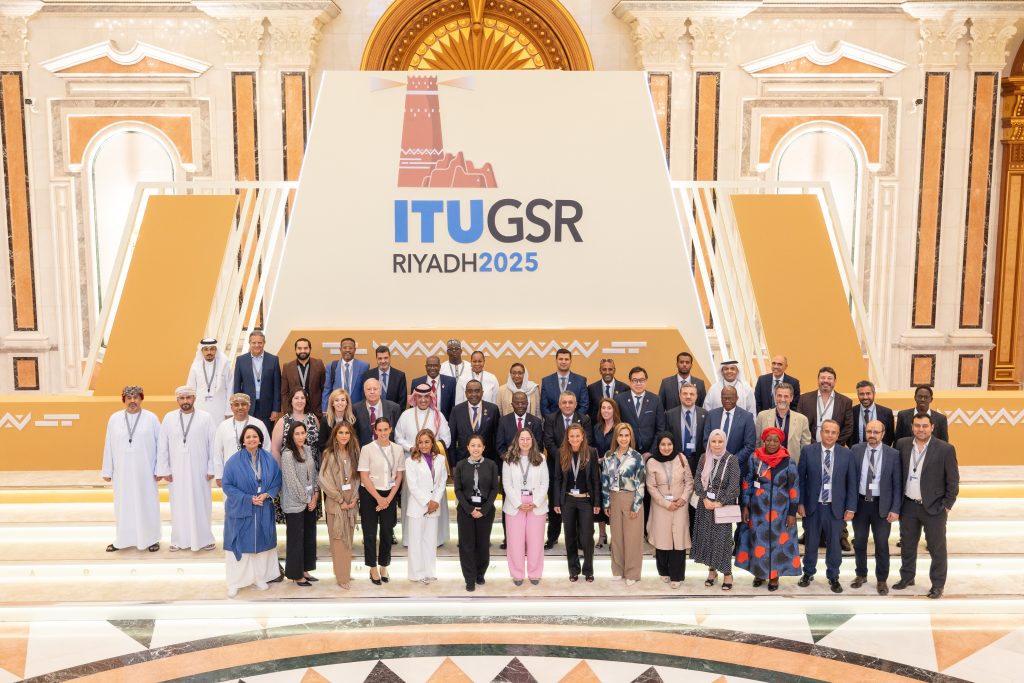
A New Regulatory Vision for Digital Ecosystem Builders in Saudi Arabia The Global Symposium for Regulators (GSR) 2025, held in Riyadh, Saudi Arabia, introduced a new strategic direction for telecom and ICT regulators. Through a set of carefully crafted, non-binding Best Practice Guidelines, the International Telecommunication Union (ITU) encourages regulators to move from traditional oversight […]
RED Cybersecurity Requirements – Is Your Product Ready?
Europe’s new RED Cybersecurity Requirements under Delegated Act (EU) 2022/30 come into force on 1 August 2025, creating significant obligations for manufacturers and distributors of radio equipment. Understanding whether these requirements apply to your product and ensuring readiness is crucial. Let’s be clear: Non-compliance by 1 August 2025 means suspension of EU market access. Enforcement […]
REDCA May 2025: Key EU Radio Equipment Regulatory Updates
Introduction: The Importance of REDCA May 2025 for Radio Equipment Regulation The Radio Equipment Directive Committee (REDCA) meeting held on May 14, 2025, represents a critical milestone in the evolution of radio equipment regulation in the European Union. This gathering of regulatory authorities, industry experts, standardization bodies such as ETSI, and the European Commission focused […]
Cybersecurity Essentials for a Safer Digital Life
In today’s hyper-connected world, cybersecurity essentials are no longer optional—they’re critical for protecting everything from smart home devices to medical equipment. This comprehensive guide reveals:
🔹 Real-world vulnerabilities – How hackers exploited Bluetooth flaws to remotely unlock smart locks (2022) and why the “KRACK” attack forced Wi-Fi security upgrades worldwide
🔹 Industry-specific threats – From the Jeep Cherokee hack (2015) that triggered a 1.4M vehicle recall to ransomware attacks compromising 1.3M patient records
🔹 Proven protection strategies – Essential steps including:
Signal-blocking pouches for key fobs
Mandatory two-factor authentication
AI-driven fraud detection for financial systems
🔹 Emerging risks – How quantum computing and 5G networks are creating new attack surfaces
Packed with verified case studies and actionable advice, this article delivers the cybersecurity essentials every individual and organization needs to survive in our wireless world.